 NexMask-官方博客
Where to Use Short-Term Email Addresses
The core design of a short-term email address is to receive emails within minutes to a few days and then self-destruct. It is suitable for these scenarios:
One-time downloads or coupon claims
When downloading whitepapers, ebooks, or discount codes, websites require an email address, and subsequent marketing emails will flood your inbox. Use a short-term email to receive the download link or verification code, and it self-destructs afterward. Your primary email is never exposed.
Trying non-core services
When testing a tool or subscribing to content, you only need to receive one activation email and do not plan to continue after the trial. A short-term email receives the activation link and clears the trial records upon expiration.
Form testing and QA
Developers and operations staff need to batch-test registration flows, email sending logic, or multi-account behavior. Short-term emails can quickly generate many addresses and automatically clean up after testing, leaving no test data behind.
The common thread in these scenarios: you only need to receive an email once, you won’t log into that email again, and you won’t use it to recover passwords or receive important notifications.
Scenarios Where Short-Term Email Addresses Are Not Suitable
Short-term emails have three hard boundaries, and touching any one of them will result in permanent loss of contact:
Self-destruction upon expiration prevents password recovery
After a short-term email expires, the entire inbox is destroyed, and all subsequent emails sent to that address are lost. If you used it to register a social account, game account, or paid service, clicking "Forgot Password" will send a reset link to the destroyed email, and the account is permanently lost. Any account that requires long-term maintenance cannot use a short-term email.
Some public short-term email inboxes are public
Some temporary email services lack privacy isolation mechanisms. Anyone who knows the email address or accesses the public inbox page can see the received email content. If the email contains verification codes, order information, or account activation links, third parties can directly read them and log into your account.
No outbound sending support
Most short-term emails can only receive, not send. They cannot be used to reply to emails or proactively contact others. If a service requires email confirmation of identity or two-way communication, short-term emails cannot fulfill that.
Why Mainstream Platforms Block Short-Term Email Addresses
Many internet platforms and SaaS services have integrated real-time validation APIs or open-source domain blacklists to directly detect temporary email domains when users enter their email address. These blacklist databases contain tens of thousands to over a hundred thousand temporary email domains and are continuously updated.
The blocking logic usually occurs when the registration form is submitted: after the user enters the email, the backend calls the validation interface. If the domain matches a blacklist entry, it directly returns an error message such as "Temporary email not supported" or "Please use a valid email address." Some platforms also block during the email sending stage, so even if registration succeeds, the verification email cannot be received.
The purpose of such blocking is to prevent bulk registrations, spam accounts, and trial abuse. For platforms, users with temporary emails cannot receive subsequent notifications, marketing emails, or account recovery requests, making the account value close to zero.
What to Do When Rejected or Needing Long-Term Receiving
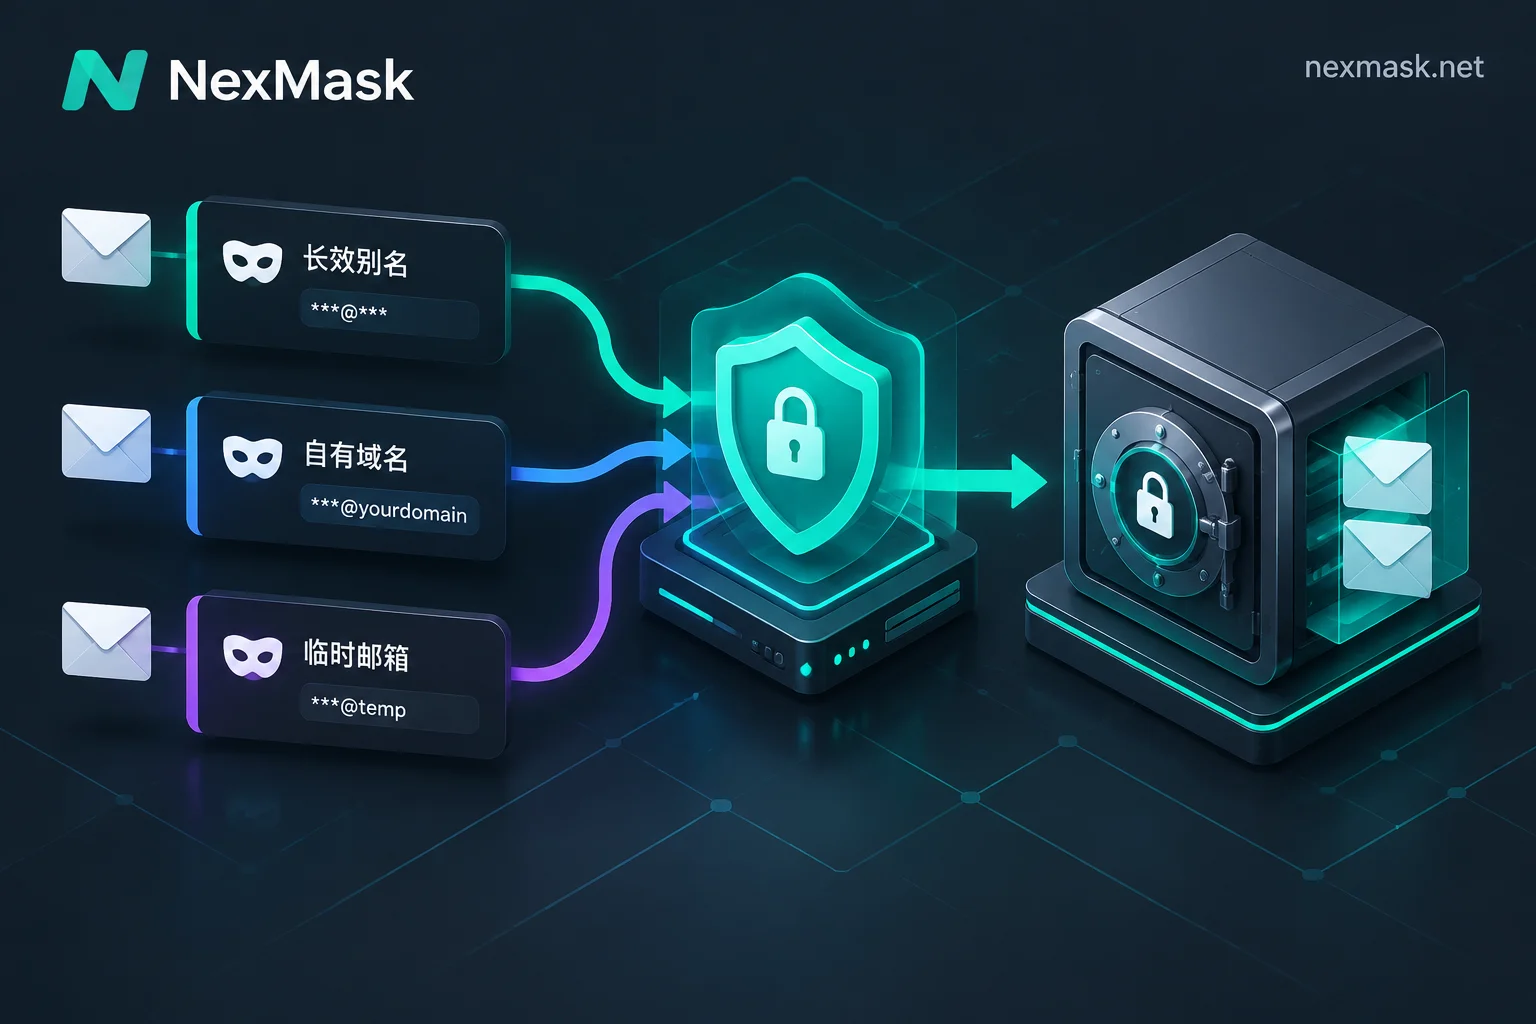
If you encounter a short-term email domain block during registration, or if the service will require long-term maintenance, notifications, and password recovery in the future, you should switch to a long-lived alias or custom domain.
Long-lived alias (email forwarding)
A long-lived alias is an independent email address that automatically forwards received emails to your real primary inbox. It can be used long-term and deactivated at any time. If a service starts sending spam, simply deactivate that alias without affecting your primary email or other aliases. Long-lived aliases support two-way sending and receiving, allowing you to send and reply using the alias identity. Mainstream platforms typically do not block them.
When you need a long-lived alias, you can visit NexMask Long-Lived Alias Service—one alias per site, valid until expiration, can be deactivated or restored.
Custom domain
If you need to generate aliases in bulk or have full control over the email address, you can bind your own domain. After binding, emails to any prefix will be forwarded to your primary inbox (catch-all). The domain belongs to you and can be migrated out at any time. Custom domains are usually not blocked because they are independent domains rather than public temporary email services.
To use a custom domain, you need to add MX records at your domain registrar pointing to the forwarding service. For detailed configuration steps, see NexMask Custom Domain Service.
How to Decide Between Short-Term Email and Long-Lived Alias
The core criterion is: will this email need to receive emails in the future?
- If you only need to receive a verification code or download link once and won’t log in again, use a short-term email.
- If you might need to recover a password, receive bills, or transaction notifications in the future, use a long-lived alias.
- If the service explicitly rejects temporary emails, use a long-lived alias or custom domain directly.
The advantage of short-term emails is no registration, immediate use, and self-destruction upon expiration—suitable for low-risk instant scenarios. The advantage of long-lived aliases is long-term stability, deactivatable, and two-way sending/receiving—suitable for accounts requiring continuous maintenance. They solve different problems; neither replaces the other. Choose based on your needs.


Comments(0)