 NexMask-官方博客
How Anonymous Temporary Emails Work and Their Applicable Boundaries
The core features of anonymous temporary emails are no registration, independent operation, and automatic destruction upon expiration. Emails only stay in the temporary session inbox and do not flow to or associate with your real primary email. After claiming a temporary email address, you can receive emails within its validity period. Once the session ends or expires, the entire mailbox and its emails are destroyed together and cannot be recovered.
This mechanism makes it suitable for scenarios that require no follow-up maintenance, such as receiving one-time verification codes, trying low-trust websites, and downloading whitepapers. When you only need to complete a single registration verification and do not plan to log in again or receive any further emails, a temporary email can prevent your real email address from being exposed.
But the destruction mechanism also brings a fatal flaw: once the mailbox is destroyed or the session expires, any subsequent notifications, second-factor verification codes (2FA), and password recovery emails cannot be delivered. For anything involving paid subscriptions, important account binding, or platforms requiring long-term login, temporary emails are strictly prohibited. You cannot use a destroyed mailbox to recover a password, nor can you receive subscription renewal notices or billing reminders.
How Websites Block Disposable Temporary Emails
Target websites mainly rely on three technical methods to block temporary emails. When combined, their coverage is quite broad:
Domain blacklist comparison: Open-source projects (such as disposable-email-domains on GitHub) and commercial services (such as WhoisXML API) maintain lists of tens of thousands to hundreds of thousands of known disposable email domains. When a user submits an email address, the website extracts the domain part and compares it against the blacklist, rejecting it on a match. This is the most direct and broadest blocking method.
MX record fingerprinting: Even if temporary email providers constantly rotate new domains, as long as the MX records of those domains point to known temporary mail servers, they can be identified. Websites query the MX resolution results of the email domain and compare them against known temporary mail server IP ranges or hostname patterns. This method can identify new domains that have not yet entered a blacklist but are already in use.
Domain registration age and heuristic scoring: Domains registered recently, with abnormal DNS configurations, or lacking valid SPF/DKIM records are flagged as high risk. Some websites combine domain age, WHOIS information, and historical email delivery reputation to produce a risk score, rejecting anything below a threshold.
When you see a "Disposable email detected" or "Invalid email" prompt, it usually means one or more of the above rules has been triggered. Continuing to switch public temporary domains often still gets blocked, because blacklists update quickly and MX fingerprinting covers all domains of the same provider.
Alternatives When You Encounter Rejection
When registration is rejected by a target website for using a disposable email, the effective solution is to switch to a long-lasting alias or an alias bound to an independent custom domain.
Long-lasting alias: A long-lasting alias forwards emails as-is to your commonly used real mailbox and supports replying and sending as the alias identity. As long as you do not manually deactivate it, the alias can keep receiving emails and can complete password recovery and second-factor verification. When an alias suffers a data breach or spam harassment, you can deactivate that single alias, protecting your real email privacy while avoiding account lockout. Long-lasting alias domains are usually not on public disposable email blacklists and can pass email validation on most websites.
Custom domain alias: If you own an independent domain, you can bind it to an alias service. After configuring MX records, you can generate alias addresses with any prefix using that domain. A custom domain has independent MX records and domain reputation, will not trigger public disposable email blacklist rules, and will not be blocked by MX fingerprinting. The domain belongs to you and can be migrated to other email service providers at any time, making it suitable for long-term use and scenarios with higher privacy requirements.
If the platform you are registering for has long-term maintenance needs (such as SaaS services, cloud provider accounts, or social platforms), or may involve paid subscriptions and password recovery, you should use a long-lasting alias from the start rather than a temporary email. Temporary emails are only suitable for scenarios where you are certain you will not need to receive follow-up emails.
Selection Boundary Between Temporary Emails and Long-Lasting Aliases
The essential difference between temporary emails and long-lasting aliases lies in email flow and lifecycle management:
- Temporary email: Emails stay in an independent session inbox, the entire mailbox is destroyed upon expiration, and it is not associated with your real email. It is suitable for one-time verification code receipt, low-trust website trials, form testing, and other scenarios requiring no follow-up maintenance. You can claim one at any time without registration, but it cannot be used for accounts that need long-term email receipt or password recovery.
- Long-lasting alias: Emails are forwarded as-is to your commonly used real mailbox, and you can send and reply as the alias identity. As long as it is not deactivated, it can keep receiving emails. It is suitable for platforms requiring long-term login, password recovery, and subscription notifications, as well as scenarios where you want one email address per site. When an alias suffers spam harassment or a data breach, you can deactivate that alias alone without affecting other accounts.
If the service you are registering for may generate follow-up notifications (billing, renewal reminders, security alerts) or requires password recovery, choose a long-lasting alias; if you are just downloading a whitepaper, trialing a low-trust service once, or testing a form, a temporary email is enough.
Scenarios requiring batch generation of temporary emails, multi-target forwarding, or custom domain features usually require membership privileges.
Claim an Anonymous Temporary Email or Set Up a Long-Lasting Alias
Choose the tool according to your actual needs:
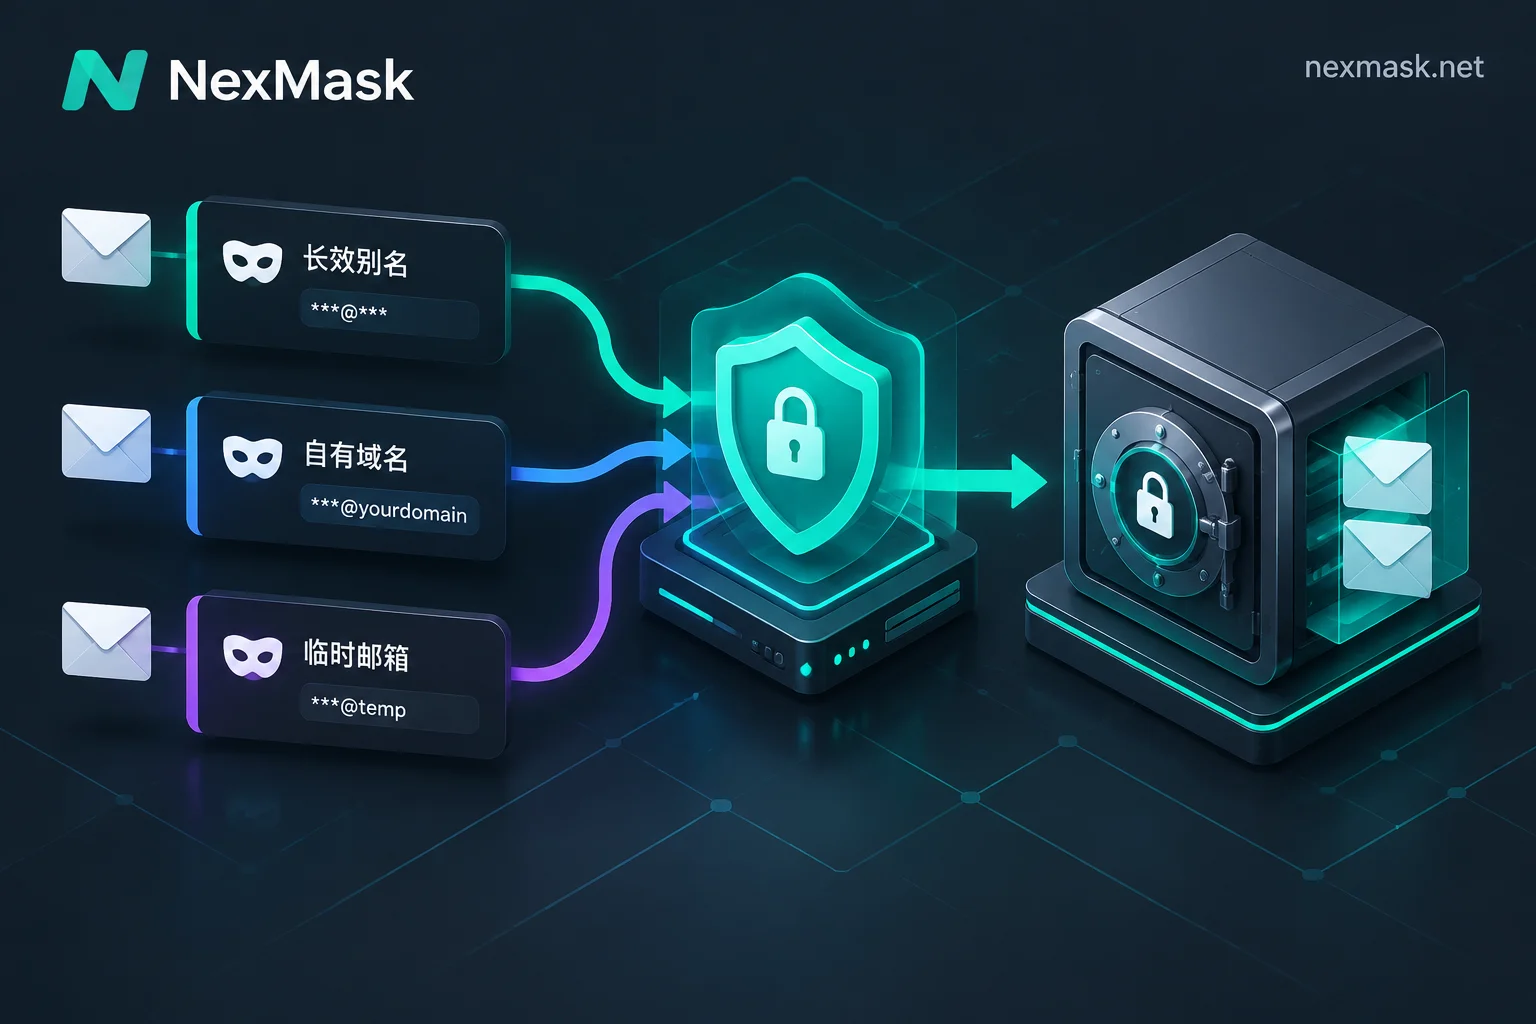
- If it is for one-time verification code receipt or a low-trust website trial, you can claim a temporary anonymous email, usable without registration and automatically destroyed upon expiration.
- If you need to register for a service requiring long-term login or password recovery, or have encountered temporary email rejection, you should set up a long-lasting alias, with emails forwarded to your commonly used mailbox. It can be deactivated but will not be automatically destroyed.
- If you need to bypass public domain blacklists or achieve completely independent domain reputation management, you can bind a custom domain to generate aliases.
Zero logs, no IP recording. Specific expiration times and membership feature quotas are subject to the official website.


Comments(0)